Cybersecurity Awareness Month | October 2026
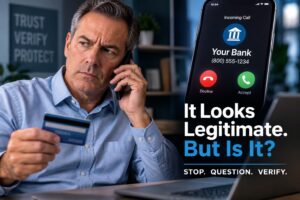
Your bank calls.
The caller knows your name.
They tell you there’s suspicious activity on your account.
And the phone number on your screen matches the number printed on the back of your bank card.
Would you trust the call?
Most of us probably would.
And that’s exactly what makes today’s scams so effective.
Cybercriminals don’t always need to hack their way into an account or break through a firewall.
Sometimes they just need you to believe them.
Would You Question It? Your Bank Is Calling
Your phone rings.
The caller ID shows the name of your bank.
The person on the other end says they’re calling from the fraud department. There’s been suspicious activity on your account.
They mention a transaction.
“Did you authorize this?”
You didn’t.
Now you’re concerned.
But you’re also suspicious enough to check.
While you’re talking, you turn over your debit or credit card and look at the customer-service number printed on the back.
It matches the number on your phone.
That feels like confirmation.
The call must really be from your bank.
Except it isn’t.
A criminal can make the number displayed on your phone appear to be a legitimate number—even your bank’s.
Now the caller has something important.
Your trust.
Then They Offer to “Help”
The caller tells you they need to secure your account.
Maybe they already know some information about you.
Then a security code arrives on your phone.
“I just sent you a verification code. Read that back to me so I can confirm your identity.”
That sounds reasonable.
Banks use verification codes all the time.
But that code may actually be what the criminal needs to access your account.
Or maybe a notification appears asking you to approve a login.
Maybe you’re told your account has been compromised and your money needs to be moved somewhere “safe.”
The details can change.
The strategy doesn’t.
Make it look legitimate. Create urgency. Gain your trust. Get you to act.
STOP. QUESTION. VERIFY.
STOP. Don’t let the urgency of the situation make the decision for you.
QUESTION. Why does the caller need the code that was sent directly to your phone? Why are you being asked to approve something you didn’t initiate? Why would your bank need you to move money somewhere else?
VERIFY. Hang up. Then call the number on the back of your card yourself, or contact your bank through its official app or website.
There’s an important difference.
You initiated the trusted connection instead of trusting the connection that came to you.
What Does This Have to Do With Your Business?
Quite a bit.
Because we make assumptions about our business technology every day, too.
“Our computers are working, so we’re fine.”
Maybe.
But are they receiving security updates?
Is endpoint protection installed and working?
Is someone monitoring for problems?
A computer can work perfectly well and still have a security vulnerability.
“We have backups.”
That’s good.
But when was the last time someone verified that the backups completed successfully?
More importantly, when was the last time someone tested whether the data could actually be restored?
A backup you can’t recover isn’t much of a backup.
“We have MFA.”
Excellent.
But is multi-factor authentication protecting everyone and everything it should?
And would an employee recognize an unexpected MFA request as something that needs to be questioned rather than approved?
“Our employees know not to click suspicious emails.”
That’s important.
But today’s social engineering isn’t limited to badly written emails.
Would an employee question a phone call from their bank if the number matched?
What if the caller sounded exactly like the CEO?
We’ll talk about that one next.
“Our IT company handles cybersecurity.”
Hopefully they do.
But what does that actually mean?
What are they monitoring?
What happens when an alert occurs?
Who responds after hours?
Are vulnerabilities being identified and addressed?
Are backups being tested?
When was the last time someone reviewed your entire environment with you?
You shouldn’t have to understand every technical detail.
But you should be able to get clear answers.
Don’t Confuse “Looks Right” With “Verified”
That’s really the lesson.
Your bank’s phone number looks right.
Your computers look like they’re working.
Your backups show that they’re running.
Your security software is installed.
Everything may be perfectly fine.
But cybersecurity shouldn’t depend entirely on assumptions.
Verify.
That doesn’t mean becoming suspicious of everything.
It means knowing which things are important enough to double-check.
Money.
Passwords.
Security codes.
Changes to banking information.
Unexpected login requests.
Sensitive information.
And the technology your business depends on every day.
Your Employees Don’t Need to Become Cybersecurity Experts
Neither do you.
People simply need permission to question something that doesn’t feel right.
That’s important in a business environment.
Employees sometimes hesitate to question a request because they don’t want to inconvenience a customer, vendor, manager—or the CEO.
We want the opposite.
If something involves money, credentials, sensitive information or an unusual request:
Take the extra minute.
Stop.
Question.
Verify.
A legitimate person won’t mind that you’re protecting the organization.
Five Questions Worth Asking About Your Business
You don’t need a 50-page cybersecurity report to start asking better questions.
Start here:
- Do we know what’s connected to our network and who has access to our systems?
- Are our computers and other devices being updated, protected and monitored?
- Have we actually tested whether our backups can be restored?
- Is multi-factor authentication protecting the accounts that need it?
- Would our employees feel comfortable stopping and verifying an unusual request—even if it appeared to come from someone important?
If you can confidently answer all five, great.
If you can’t, you’ve identified a place to start.
Trust. But Verify.
Good cybersecurity doesn’t mean distrusting everyone and everything.
It means putting enough safeguards in place that one convincing phone call, one mistaken click or one overlooked piece of technology doesn’t become a major business problem.
At SpartanTec, we help organizations understand what’s happening across their technology environment, identify potential gaps and put practical protections in place.
You don’t need more technology simply for the sake of having more technology.
You need to know the technology and processes you already depend on are actually protecting you?
How Confident Are You?
If your answer is:
“I think we’re protected.”
Let’s turn that into:
“I know we’re protected.”
Talk with SpartanTec about a Visibility & Risk Assessment.
We’ll help you understand what you have, what’s working and where you may need to take action.
STOP. QUESTION. VERIFY.
SpartanTec — We Guard Your Assets.
Frequently Asked Questions
Can scammers make a phone call look like it came from my bank?
Yes. Caller ID can be spoofed, which can make an incoming call appear to come from a legitimate organization or phone number. A familiar caller ID should not be the only way you verify someone’s identity.
Should I give a verification code to someone who says they’re calling from my bank?
Be cautious with any unexpected caller asking for a security or verification code. End the call and contact your financial institution yourself using the number printed on your card, its official app or another trusted method.
What is social engineering in cybersecurity?
Social engineering is when an attacker manipulates someone into taking an action such as providing information, sending money, sharing credentials or granting access. Attackers commonly use urgency, fear, authority and familiarity to make requests appear legitimate.
How can a business know if its cybersecurity is actually working?
Businesses should regularly verify that security controls are properly configured and functioning. That can include reviewing endpoint protection, software updates, multi-factor authentication, backups, security monitoring, user access and employee awareness.
Are backups enough to protect a business from ransomware?
Backups are an important part of ransomware preparedness, but having backups alone isn’t enough. Organizations should verify that backups are completing successfully, protect backup systems from unauthorized access and periodically test whether data can actually be restored.
Why are software updates important for business cybersecurity?
Software updates frequently address known security vulnerabilities. Businesses should have a process for keeping computers, servers, applications, firewalls and other technology current rather than relying solely on individual employees to install updates.

