Cybersecurity Awareness Month | October 2026
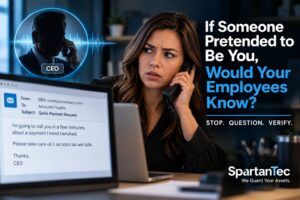
Imagine one of your employees gets an email from you.
It says: “I’m going to call you in a few minutes about a payment I need handled.”
Nothing about the message seems unusual.
A few minutes later, their phone rings.
It sounds like you.
The caller knows the name of a vendor your company works with. They know you’re traveling this week. They mention a project your team has been working on.
And they need something handled quickly before they go into a meeting.
Maybe it’s an invoice that needs to be paid. Maybe a wire needs to be sent. Maybe a vendor has “changed banks” and the payment information needs to be updated.
Your employee wants to help.
After all, you’re the boss—and you just asked them to take care of it.
There’s only one problem.
You never sent the email. You never made the call.
Someone is pretending to be you.
Would your employee know what to do next?
This Is No Longer Just an Email Problem
For years, businesses have warned employees to watch for suspicious emails: strange wording, unexpected attachments, misspelled domains and unusual requests.
That still matters. But social engineering has become more convincing.
An attacker may combine email, phone calls, text messages and information found online to make a request feel normal.
AI can also make voice impersonation more convincing.
The employee may hear a familiar voice, recognize the way you speak and be given details that make the request seem credible.
The goal isn’t necessarily to fool someone with a perfect impersonation. It’s to create enough familiarity and urgency that they act before they verify.
How Much Would Someone Need to Know About You?
Probably less than you think.
Think about how much information about your business may already be public.
- Your name and title
- Names of employees or leadership
- Vendors and business partners
- Upcoming conferences or events
- Company projects and announcements
- Photos and social media posts
- Videos, webinars, podcasts or interviews where your voice can be heard
None of that information is necessarily sensitive by itself.
But combined, it can help someone build a believable story.
An attacker might know that you’re attending a conference, know who handles accounting and know the name of a vendor your company uses.
Now imagine the employee receives an email from “you,” followed by a phone call from someone who sounds like you and knows those details.
The employee isn’t necessarily ignoring an obvious warning sign.
The attacker is deliberately removing the warning signs.
Give Your Employees Permission to Question You
This may be one of the most important things leadership can do.
Employees are often taught to be responsive. Help the customer. Take care of the vendor. Get the CEO what they need.
That’s usually a good thing.
But it can become a problem when an employee believes questioning an unusual request might make them look difficult, slow or unhelpful.
Your team should know that if a request involves money, credentials, sensitive information or a change to a normal process, they have permission to stop—even when the request appears to come from you.
In fact, that’s exactly what you want them to do.
STOP. QUESTION. VERIFY.
STOP. Don’t let a title, familiar voice or urgent deadline rush the decision.
QUESTION. Is this request normal? Why is the process changing? Why does it have to happen immediately?
VERIFY. Use a different, already-trusted method before taking a high-risk action.
A familiar voice should no longer be the only proof you need before taking a high-risk action.
Verification Needs to Be Independent
If the request came by email, don’t simply reply to that email.
If the caller gives you a phone number, don’t use that number to verify the caller.
Instead, use a communication method your employee already trusts.
- Call the executive using a known phone number.
- Send a message through the company’s established communication platform.
- Follow the normal financial approval process.
- Independently contact a vendor before changing banking information.
- Require a second person to approve certain financial transactions.
The point is simple: the person making the request should not control how the request is verified.
Would Your Process Stop the Payment?
Employee awareness is important, but your protection shouldn’t depend entirely on one person recognizing a scam.
Your business processes should provide another layer of protection.
Ask yourself:
- Can one employee receive a payment request and complete the transaction without another approval?
- Are vendor banking changes independently verified using known contact information?
- Do larger wires or payments require a second approval?
- Do employees know exactly what to do when an executive request feels unusual?
- Would your employees feel comfortable delaying a request long enough to verify it?
If the answer to one or more of those questions makes you uncomfortable, that’s useful information.
You’ve found a process worth strengthening.
Your Employees Can Be One of Your Strongest Cybersecurity Controls
We don’t like calling employees the “weakest link.”
A well-prepared employee can be the person who notices that something doesn’t add up, stops a fraudulent payment, questions an unexpected login request or calls IT before clicking.
The goal isn’t to make everyone suspicious of every request.
It’s to make verification normal.
Cybersecurity awareness and practical security processes work best together.
Employees need to know what to watch for. Leadership needs to create processes that support them. Technology should provide another layer of protection.
That’s how people, process and technology work together.
Four Things Worth Verifying Every Time
For leadership, the rule can be simple. Slow down and independently verify unusual requests involving:
- Money
- Credentials or security codes
- Sensitive information
- Changes to normal procedures
You don’t need to turn every transaction into an investigation.
You just need a clear point where someone is expected to stop and verify before the risk becomes real.
Cybersecurity Isn’t Only About Keeping Someone Out of Your Network
Sometimes the attacker never needs to get into your network.
They may simply try to convince someone inside your organization to do what they want.
Send the payment.
Change the banking information.
Share the password.
Approve the login.
Open the door.
That’s why cybersecurity isn’t only a technology issue.
It’s also about making sure your employees know what to do when something that looks completely legitimate…isn’t.
Would Your Employees Know?
Ask your team one question:
If you received an unusual request from me involving money, credentials or sensitive information, how would you verify that it was really me?
Their answers may tell you a lot about how prepared your organization really is.
If you’re not sure whether your employees and processes would stop a convincing impersonation attempt, let’s find out.
STOP. QUESTION. VERIFY.
SpartanTec — We Guard Your Assets.
Frequently Asked Questions
What is CEO impersonation fraud?
CEO impersonation fraud is a social engineering attack in which a criminal pretends to be an executive or other trusted leader to convince an employee to send money, change payment information, share credentials or take another sensitive action.
Can AI be used to imitate someone’s voice?
AI tools can be used to create convincing voice imitations from available audio. Businesses should not rely on a familiar-sounding voice alone when verifying high-risk requests.
What should an employee do if an executive makes an unusual payment request?
Pause the transaction and independently verify the request using a known phone number, established company communication channel or normal approval process. Do not rely only on contact information supplied in the request.
How can businesses prevent fraudulent vendor banking changes?
Use a documented verification process. Independently contact a known vendor representative using previously established contact information and consider requiring a second approval before changing payment details.
Are employees the weakest link in cybersecurity?
Employees can be an important cybersecurity control when they understand common attack methods, know when to question unusual activity and have clear procedures for verifying sensitive requests.
What is social engineering?
Social engineering is the use of manipulation, urgency, authority, familiarity or other techniques to convince someone to reveal information, provide access or take an action that benefits an attacker.

